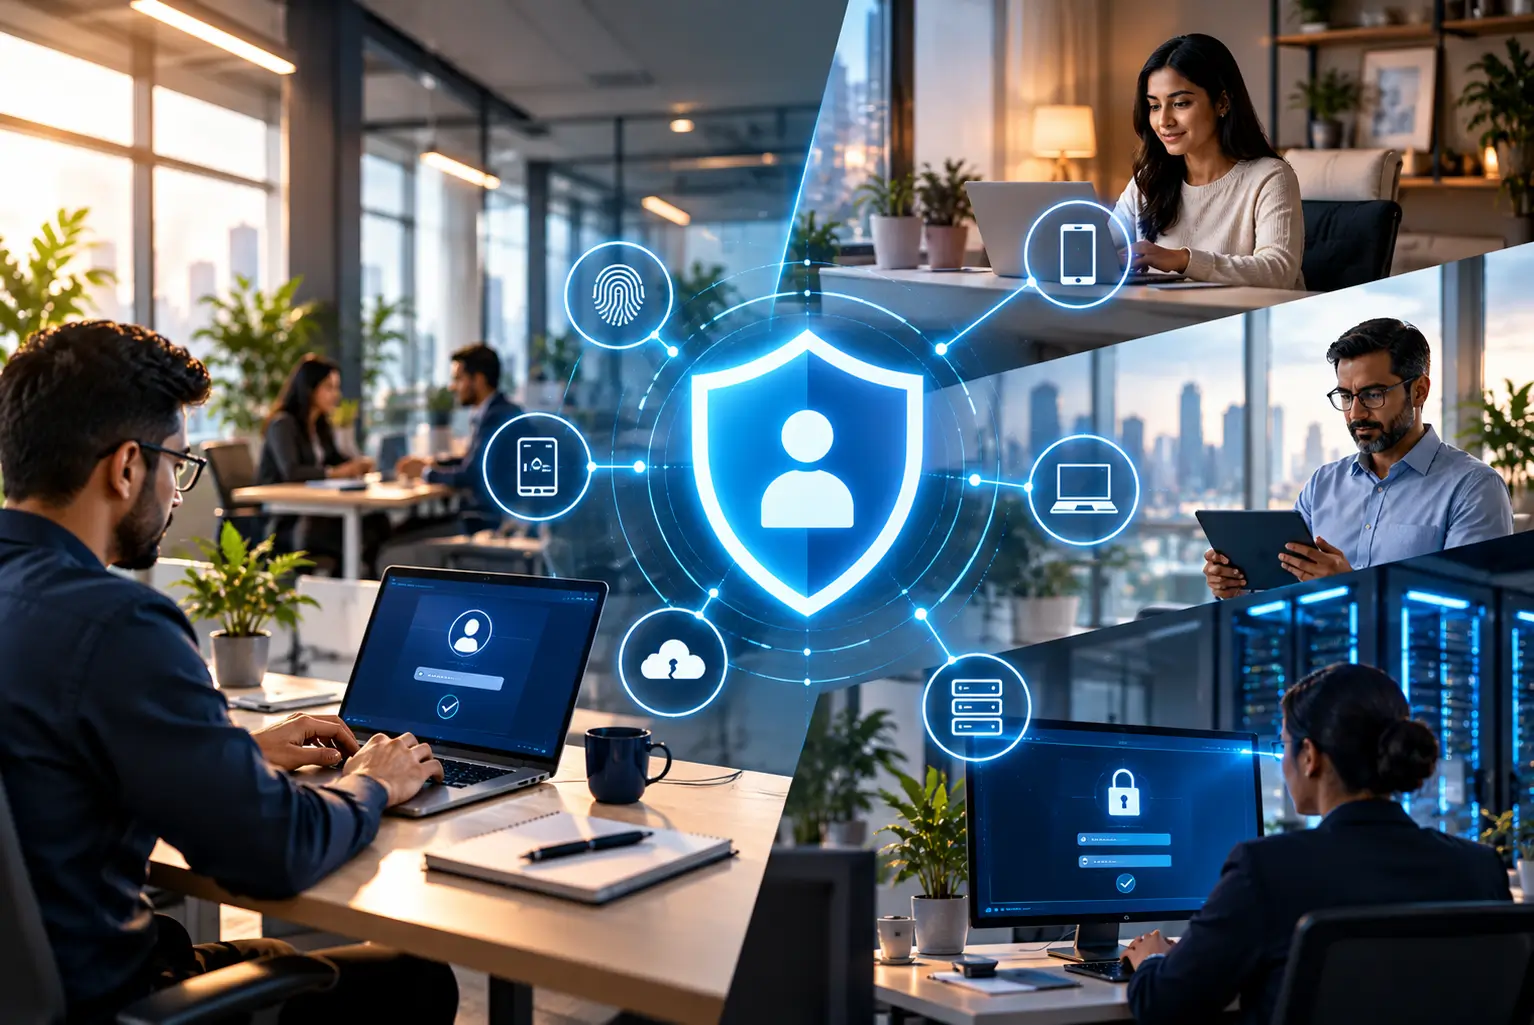
The core IAM best practices for hybrid work are: enforce phishing-resistant MFA everywhere, use conditional access to check device and risk on every sign-in, apply least privilege and just-in-time access, consolidate apps behind single sign-on, and protect privileged accounts with PAM. Together they make identity the strong perimeter that the office network no longer is.
Why identity is the new perimeter
The data is unambiguous. Around 22% of breaches involve stolen credentials and roughly 60% involve a human element such as phishing or error (Verizon 2025 DBIR) — yet Microsoft research finds that multi-factor authentication alone blocks over 99% of automated account-compromise attacks. Identity is both the most-attacked surface and the most defensible one.
In the office era, security assumed the network was the boundary: inside was trusted, outside was not. Hybrid work demolished that assumption. People sign in from home Wi-Fi, airports and personal devices, and your data lives in cloud apps you do not host. The one thing present in every interaction is identity — which is exactly why attackers target it. Strong identity and access management is now the foundation of enterprise security.
Start with MFA (but the right kind)
Multi-factor authentication remains the single most effective control against account takeover, blocking the overwhelming majority of identity attacks. But not all MFA is equal:
- Avoid SMS and voice codes where you can — they are phishable and SIM-swappable.
- Prefer app-based push with number matching, and move high-risk users to phishing-resistant MFA (FIDO2 security keys, Windows Hello for Business, passkeys).
- Enforce it everywhere — every user, every app, no exceptions for “convenience” accounts, which are the ones attackers find.
Conditional access: verify every request
MFA answers “is this the right person?” Conditional access answers “should this person, on this device, from here, right now, get access to this?” It evaluates signals on every sign-in and decides: allow, allow with MFA, require a compliant device, or block.
Practical policies to start with:
- Require MFA for all users, and block legacy authentication protocols that bypass it.
- Require a managed, compliant device for access to sensitive apps — which ties identity to your device management & UEM and endpoint security.
- Raise friction on risky sign-ins (impossible travel, anonymous IPs) and step up verification automatically.
Least privilege and just-in-time access
Most users have far more access than their job needs, and that standing access is what an attacker inherits the moment an account is compromised. Least privilege fixes this:
- Grant the minimum access required for a role, and review it regularly.
- Use just-in-time elevation — privileges are granted for a task, for a time window, then revoked, not held permanently.
- Run periodic access reviews so entitlements do not quietly accumulate as people change roles.
Least privilege does not stop a breach; it decides how bad the breach gets.
Single sign-on and lifecycle automation
Single sign-on (SSO) is both a security and productivity win: one strong, monitored identity instead of dozens of passwords scattered across apps. Put every app you can behind SSO, and automate the joiner-mover-leaver lifecycle so access is provisioned on day one and — critically — removed the moment someone leaves. Orphaned accounts are a favourite attacker foothold.
Privileged access management (PAM)
Admin and service accounts are the keys to the kingdom, and they need stronger controls than ordinary users. PAM services enforce: vaulted credentials, session recording, just-in-time elevation and approval workflows for privileged actions. If you do one thing beyond MFA, protect your privileged accounts — they are what turn a minor incident into a catastrophic one.
Identity in a Zero Trust model
Every practice here is a pillar of Zero Trust security — “never trust, always verify” starts at identity. Zero Trust treats identity as the primary control plane: verify explicitly, enforce least privilege, and assume breach. If you are building toward Zero Trust, identity is where you get the most risk reduction for the least effort. Our guide to Zero Trust explained simply puts it in plain English.
A practical rollout order
You do not deploy all of this at once. A sensible sequence:
- MFA everywhere (fastest, highest impact).
- Conditional access baseline policies + block legacy auth.
- SSO consolidation and lifecycle automation.
- Least privilege and access reviews.
- PAM for privileged and service accounts.
- Move high-risk users to phishing-resistant, passwordless methods.
Each step reduces risk on its own, so you get value from day one. See how we deliver identity & access management end to end.