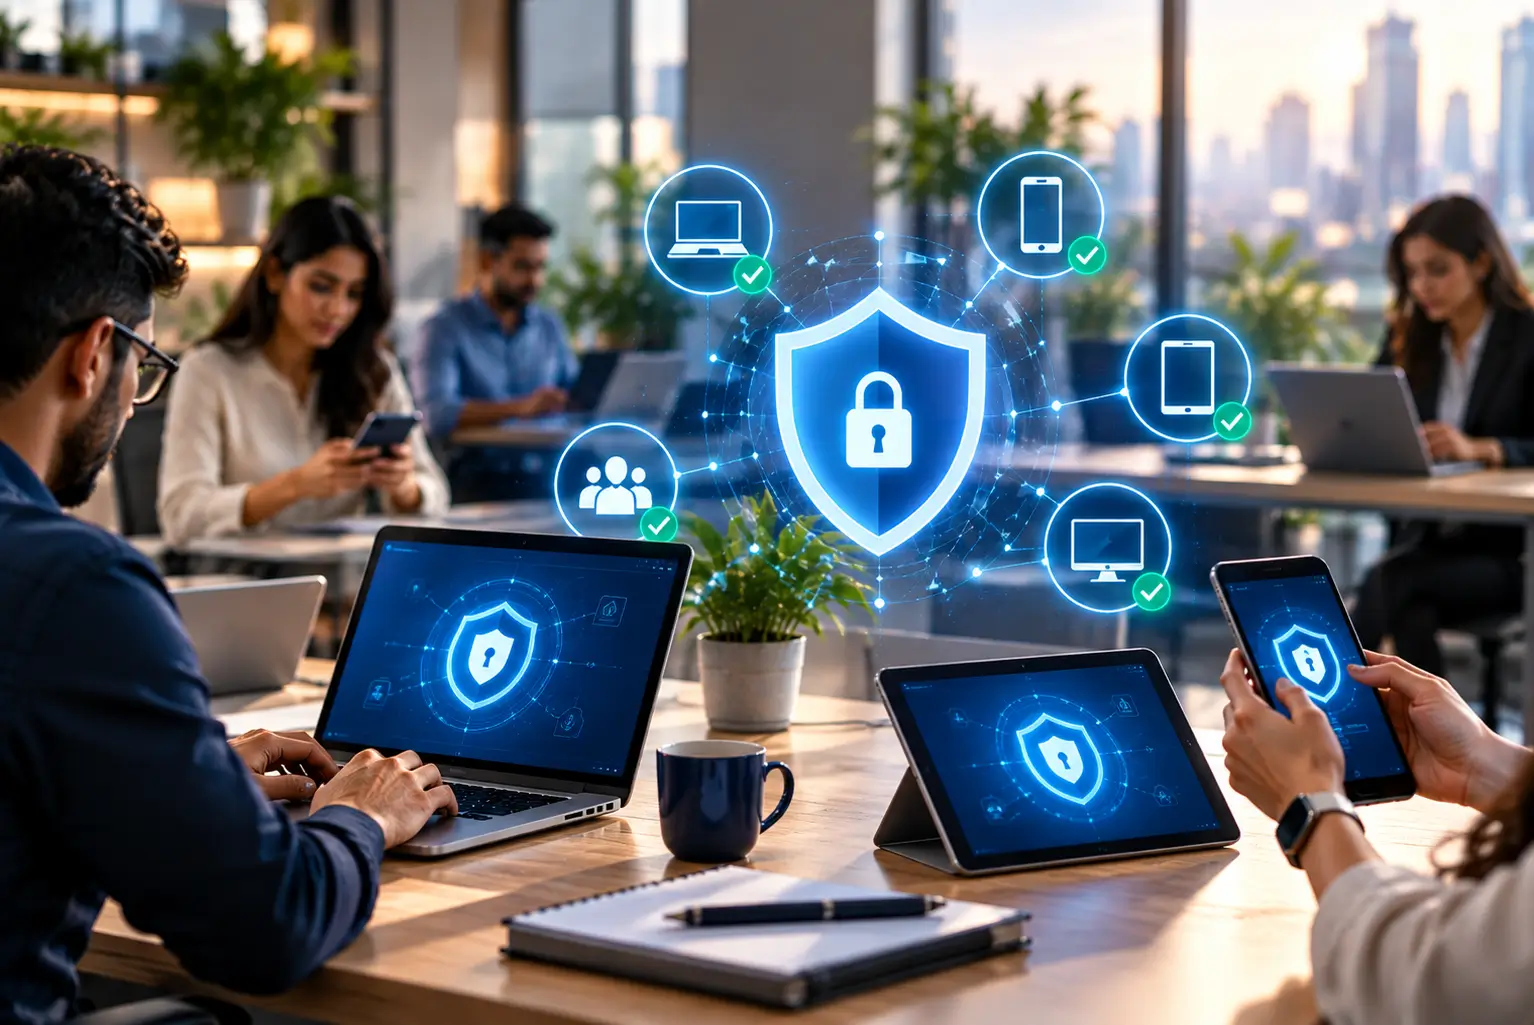
To secure endpoints in a BYOD (bring your own device) world, protect the data and the access, not just the device: deploy EDR/XDR on managed endpoints, use mobile application management to contain company data on personal phones, enforce conditional access so only healthy devices reach sensitive apps, and separate work from personal with policy. You control the corporate data; the user keeps their device.
What BYOD really changes
The risk is concentrated here. Ransomware now features in 44% of breaches, up from 32% a year earlier (Verizon 2025 DBIR), and the overwhelming majority of it reaches the business through an endpoint — increasingly one the organisation does not own.
Bring-your-own-device is now the norm, not the exception — personal phones for email and Teams, home laptops for quick tasks, contractor machines you have never seen. Each is an endpoint touching company data, and you do not own most of them. Traditional endpoint security assumed you controlled the hardware. BYOD breaks that assumption, so the strategy has to shift from “lock down the device” to “protect the data and control the access”.
Protect the data, not the device
The mental model that makes BYOD manageable: you cannot (and should not) fully control a personal device, but you can control what company data it can reach and what it can do with that data. That means:
- Keep corporate data inside protected apps that you can wipe independently of the user’s personal content.
- Stop data leaking out — block copy-paste and “save as” from work apps into personal ones.
- Gate access on device health and identity, not on who owns the device.
EDR and XDR on managed endpoints
For company-owned and enrolled devices, EDR/XDR such as Microsoft Defender for Endpoint is the core control: it detects malicious behaviour, isolates a compromised device in seconds, and feeds signals into your wider detection. This is where ransomware is caught and contained. For how EDR fits with SIEM and automation, see SIEM vs SOAR vs XDR.
MDM vs MAM: full control vs app-level control
Two tools, two levels of control — the BYOD decision usually comes down to choosing between them:
| MDM (Mobile Device Management) | MAM (Mobile Application Management) | |
|---|---|---|
| Controls | The whole device | Only the work apps & data |
| Best for | Company-owned devices | Personal (BYOD) devices |
| User privacy | Lower — IT manages the device | High — personal space untouched |
| Wipe | Full device wipe possible | Selective wipe of company data only |
| Adoption friction | Higher on personal devices | Low — users accept it readily |
For BYOD, MAM is usually the right answer: it contains and can selectively wipe company data while leaving the user’s photos, messages and apps alone. Both are delivered through device management & UEM (Microsoft Intune).
Conditional access ties it together
None of this works without a gatekeeper. Conditional access is what enforces “only a compliant, healthy device can open this sensitive app”. A personal phone with the work container and current policies gets in; a jailbroken or non-compliant device is blocked or limited. This is the same identity layer covered in IAM best practices for hybrid work — endpoint and identity security are two halves of one control.
Handling unmanaged and personal devices
Some devices will never be enrolled — contractors, occasional personal laptops. For these:
- Prefer browser-based access with session controls that block download and copy of sensitive data.
- Apply app protection policies so data stays inside managed apps even without full enrolment.
- Default to least access — unmanaged devices get the minimum they need, nothing more.
A BYOD security baseline that works
A pragmatic baseline most Indian enterprises can adopt:
- EDR/XDR on all company-owned endpoints.
- MAM / app protection for company data on personal mobiles.
- Conditional access requiring compliant devices for sensitive apps.
- MFA and identity controls on every sign-in.
- Selective wipe on offboarding or device loss.
- Clear data-loss prevention aligned with information protection & governance.
Explore our endpoint security services and device management & UEM to put this baseline in place.